Home / Past papers / MAD2 End Term / this paper
IIT M FOUNDATION DIPLOMA AN EXAM - 22 Dec 2024
Text of the picture (copyable)
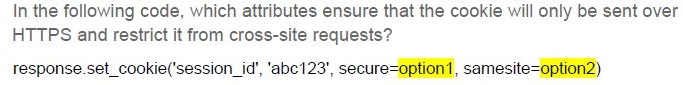
In the following code, which attributes ensure that the cookie will only be sent over HTTPS and restrict it from cross-site requests?

```
response.set_cookie('session_id', 'abc123', secure=option1, samesite=option2)
```- secure=False and samesite='Strict'
- secure=True and samesite='None'
- secure=True and samesite='Strict'
- secure=False and samesite='Lax'
- Long polling opens multiple connections between the client and the server,and the server continuously sends updates to the client in real-time.
- Long polling allows the client to make a single request to the server, where theserver holds the connection open until new data is available and then sends the response.
- Long polling involves the client repeatedly sending requests at fixed intervalsto the server to check for updates, regardless of whether new data is available.
- Long polling uses WebSockets to maintain a persistent, bidirectionalconnection between the client and the server.
Text of the picture (copyable)
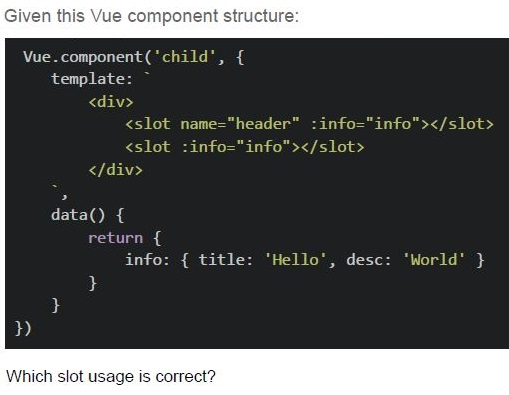
Given this Vue component structure:

```javascript
Vue.component('child', {
  template: `
    <div>
      <slot name="header" :info="info"></slot>
      <slot :info="info"></slot>
    </div>
  `,
  data() {
    return {
      info: { title: 'Hello', desc: 'World' }
    }
  }
})
```

Which slot usage is correct?
text
```html
<template v-slot:header="data">{{data.title}}</template>
```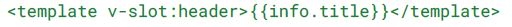
text
```html
<template v-slot:header>{{info.title}}</template>
```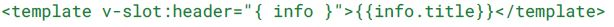
text
```html
<template v-slot:header="{ info }">{{info.title}}</template>
```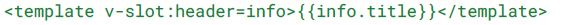
text
```html
<template v-slot:header=info>{{info.title}}</template>
```
Text of the picture (copyable)
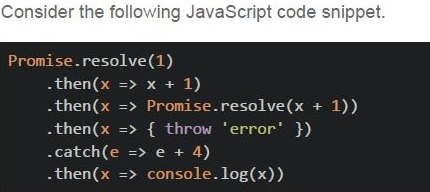
Consider the following JavaScript code snippet.

```javascript
Promise.resolve(1)
  .then(x => x + 1)
  .then(x => Promise.resolve(x + 1))
  .then(x => { throw 'error' })
  .catch(e => e + 4)
  .then(x => console.log(x))
```- 7
- error
- undefined
- error4
Text of the picture (copyable)
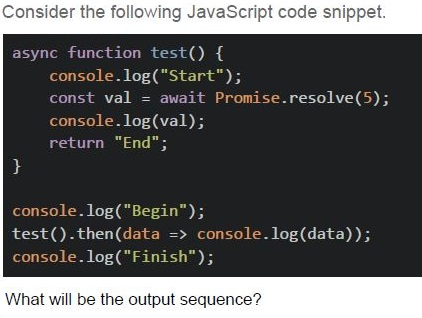
Consider the following JavaScript code snippet.

```javascript
async function test() {
  console.log("Start");
  const val = await Promise.resolve(5);
  console.log(val);
  return "End";
}

console.log("Begin");
test().then(data => console.log(data));
console.log("Finish");
```

What will be the output sequence?- Begin, Start, 5, End, Finish
- Begin, Start, Finish, 5, End
- Begin, Finish, Start, 5, End
- Begin, Finish, Start, End, 5
Text of the picture (copyable)
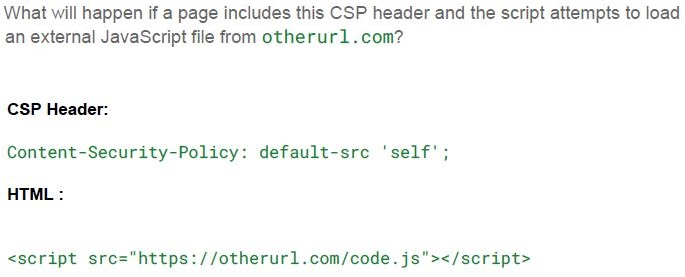
What will happen if a page includes this CSP header and the script attempts to load an external JavaScript file from otherurl.com?

**CSP Header:**

```
Content-Security-Policy: default-src 'self';
```

**HTML :**

```html
<script src="https://otherurl.com/code.js"></script>
```

text
The script from otherurl1.com will load normally.
text
The browser will display a warning and allow the script to load.
text
Nothing will happen; the CSP only affects inline scripts.

text
The script will fail to load, and an error will be logged in the console.
Text of the picture (copyable)
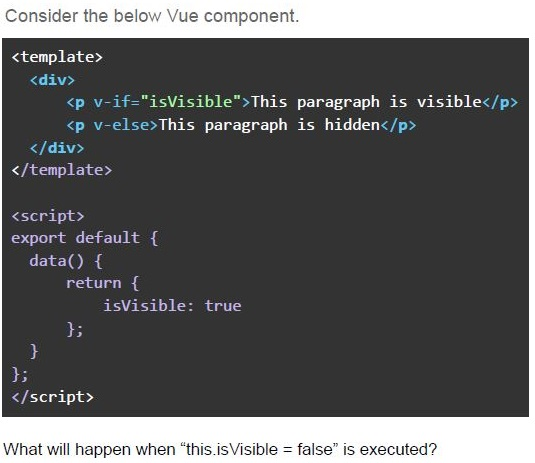
Consider the below Vue component.

```html
<template>
  <div>
    <p v-if="isVisible">This paragraph is visible</p>
    <p v-else>This paragraph is hidden</p>
  </div>
</template>

<script>
  export default {
    data() {
      return {
        isVisible: true
      };
    }
  };
</script>
```

What will happen when “this.isVisible = false” is executed?- The paragraph with the text “This paragraph is hidden” will be displayed.
- The paragraph with the text “This paragraph is visible” will be displayed.
- Both paragraphs will be displayed because of the v-if and v-else bindings.
- No change will happen, since v-if and v-else do not update the DOM.
Text of the picture (copyable)
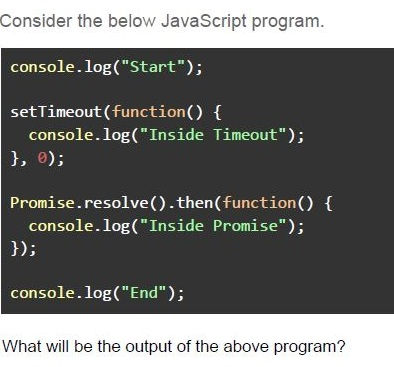
Consider the below JavaScript program.

```javascript
console.log("Start");

setTimeout(function() {
  console.log("Inside Timeout");
}, 0);

Promise.resolve().then(function() {
  console.log("Inside Promise");
});

console.log("End");
```

What will be the output of the above program?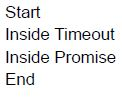
text
Start
Inside Timeout
Inside Promise
End
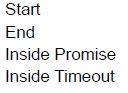
text
Start
End
Inside Promise
Inside Timeout
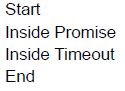
text
Start
Inside Promise
Inside Timeout
End
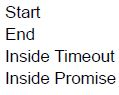
text
Start
End
Inside Timeout
Inside Promise
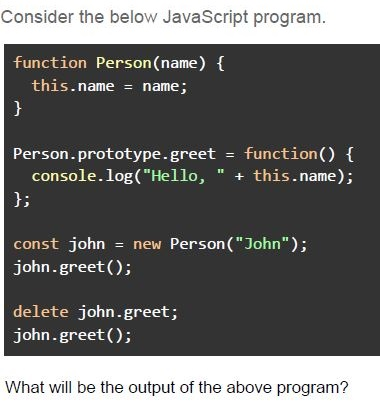
Text of the picture (copyable)
Consider the below JavaScript program.

```javascript
function Person(name) {
  this.name = name;
}

Person.prototype.greet = function() {
  console.log("Hello, " + this.name);
};

const john = new Person("John");
john.greet();

delete john.greet;
john.greet();
```

What will be the output of the above program?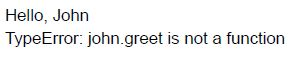
text
Hello, John
TypeError: john.greet is not a function
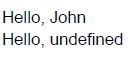
text
Hello, John
Hello, undefined

text
Hello, John
Hello, John
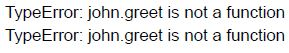
text
TypeError: john.greet is not a function
TypeError: john.greet is not a function
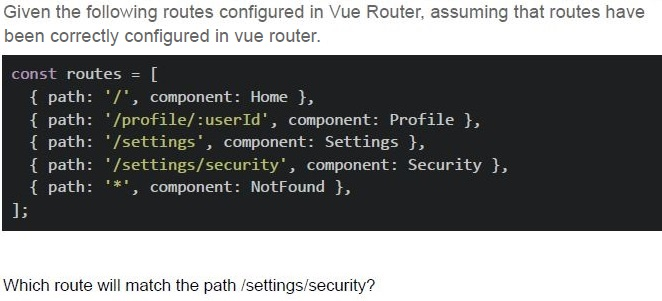
Text of the picture (copyable)
Given the following routes configured in Vue Router, assuming that routes have
been correctly configured in vue router.

```javascript
const routes = [
  { path: '/', component: Home },
  { path: '/profile/:userId', component: Profile },
  { path: '/settings', component: Settings },
  { path: '/settings/security', component: Security },
  { path: '/*', component: NotFound },
];
```

Which route will match the path /settings/security?- Home
- Profile
- Security
- Settings
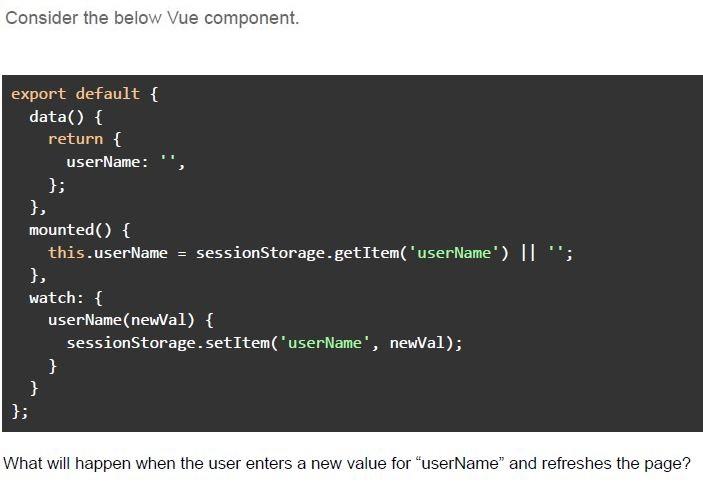
Text of the picture (copyable)
Consider the below Vue component.

```javascript
export default {
  data() {
    return {
      userName: '',
    };
  },
  mounted() {
    this.userName = sessionStorage.getItem('userName') || '';
  },
  watch: {
    userName(newVal) {
      sessionStorage.setItem('userName', newVal);
    }
  }
};
```

What will happen when the user enters a new value for "userName" and refreshes the page?- The new value will be stored in session storage, and the “userName” dataproperty will be updated.
- The new value will be stored in session storage, but the “userName” dataproperty will be reset to an empty string on page refresh.
- The “userName” data property will be reset to an empty string, and thesession storage value will be ignored on refresh.
- The “userName” data property will not be updated in session storage becausesession storage doesn't persist across refreshes.
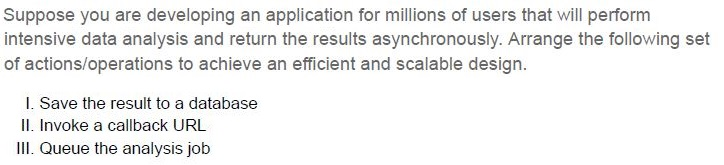
Text of the picture (copyable)
Suppose you are developing an application for millions of users that will perform intensive data analysis and return the results asynchronously. Arrange the following set of actions/operations to achieve an efficient and scalable design.

I. Save the result to a database
II. Invoke a callback URL
III. Queue the analysis job
- II, III, I
- III, I, II
- III, II, I
- I, II, III
- Cache-Control: no-store prevents caching
- Data stored in sessionStorage remains available even after the browser isclosed and reopened.
- ETag helps validate cache freshness
- localStorage has larger storage limit than cookies
- The “await” keyword can only be used inside an async function.
- The async functions run synchronously, but their await statements executeasynchronously.
- The “await” keyword pauses the execution of the surrounding async functionuntil the promise resolves.
- The async functions always return a promise, even if the return value is not apromise.
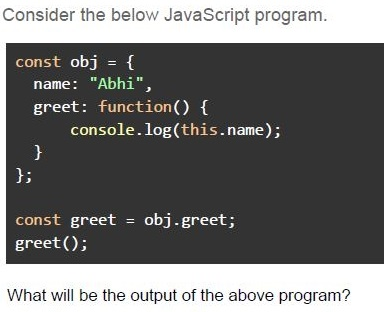
Text of the picture (copyable)
Consider the below JavaScript program.

```javascript
const obj = {
  name: "Abhi",
  greet: function() {
    console.log(this.name);
  }
};

const greet = obj.greet;
greet();
```

What will be the output of the above program?
text
Abhi

text
null
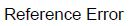
text
Reference Error
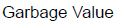
text
Garbage Value

text
undefined
- Using @app.task_periodic to run the task every 10 minutes.
- Using @app.on_periodic to schedule a periodic task.
- Using Celery Beat to schedule periodic tasks.
- Celery doesn't support scheduling tasks at fixed intervals; you need to use anexternal scheduler.
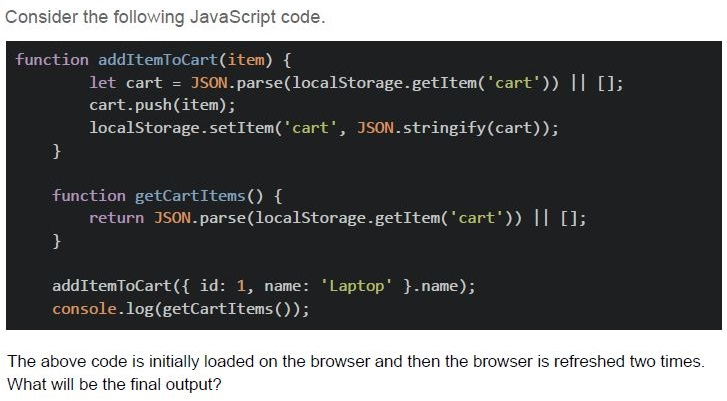
Text of the picture (copyable)
Consider the following JavaScript code.

```javascript
function addItemToCart(item) {
    let cart = JSON.parse(localStorage.getItem('cart')) || [];
    cart.push(item);
    localStorage.setItem('cart', JSON.stringify(cart));
}

function getCartItems() {
    return JSON.parse(localStorage.getItem('cart')) || [];
}

addItemToCart({ id: 1, name: 'Laptop' }.name);
console.log(getCartItems());
```

The above code is initially loaded on the browser and then the browser is refreshed two times.
What will be the final output?
text
The image shows a single vertical bar character.
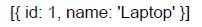
text
```
[{ id: 1, name: 'Laptop' }]
```
text
[undefined]
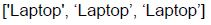
text
```
['Laptop', 'Laptop', 'Laptop']
```
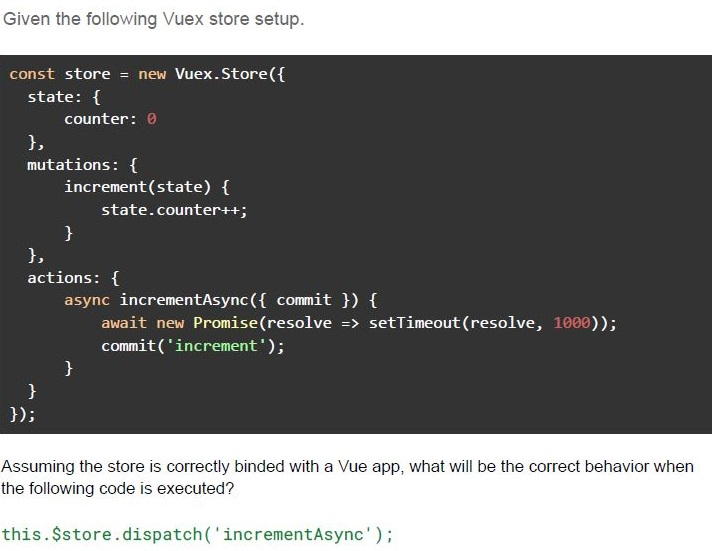
Text of the picture (copyable)
Given the following Vuex store setup.

```javascript
const store = new Vuex.Store({
  state: {
    counter: 0
  },
  mutations: {
    increment(state) {
      state.counter++;
    }
  },
  actions: {
    async incrementAsync({
      commit
    }) {
      await new Promise(resolve => setTimeout(resolve, 1000));
      commit('increment');
    }
  }
});
```

Assuming the store is correctly binded with a Vue app, what will be the correct behavior when the following code is executed?

```javascript
this.$store.dispatch('incrementAsync');
```- The increment mutation will be called immediately after the dispatch.
- The incrementAsync action will be executed synchronously, and increment willbe committed before the promise resolves.
- The state will be updated after the asynchronous operation completes.
- The action will be skipped since mutations cannot be called inside actions.
Text of the picture (copyable)
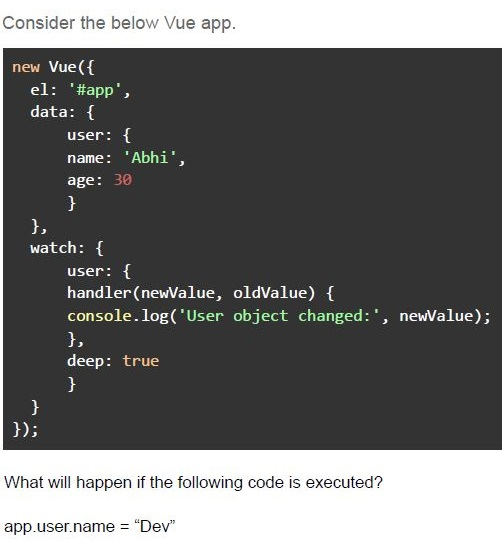
Consider the below Vue app.

```javascript
new Vue({
  el: '#app',
  data: {
    user: {
      name: 'Abhi',
      age: 30
    }
  },
  watch: {
    user: {
      handler(newValue, oldValue) {
        console.log('User object changed:', newValue);
      },
      deep: true
    }
  }
});
```

What will happen if the following code is executed?

`app.user.name = "Dev"`- The watcher will be triggered and log "User object changed: { name: 'Bob',age: 30 }".
- The watcher will not be triggered because “name” is a nested property of“user” object.
- The watcher will be triggered, but it will only log the new “name” value, i.e.,“Dev”, and not the entire user object.
- The watcher will throw an error because deep watching is not supported onnested objects.
Text of the picture (copyable)
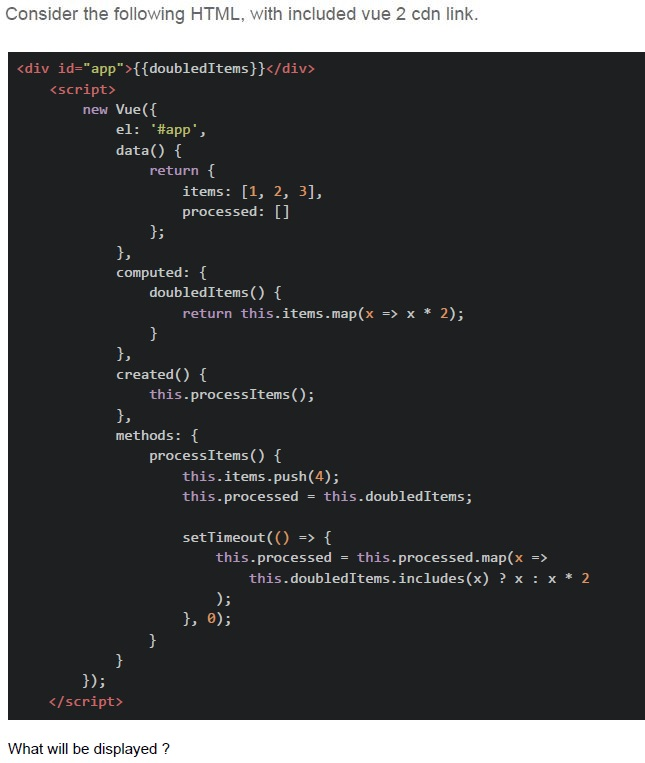
Consider the following HTML, with included vue 2 cdn link.

```html
<div id="app">{{doubledItems}}</div>
<script>
  new Vue({
    el: '#app',
    data() {
      return {
        items: [1, 2, 3],
        processed: []
      };
    },
    computed: {
      doubledItems() {
        return this.items.map(x => x * 2);
      }
    },
    created() {
      this.processItems();
    },
    methods: {
      processItems() {
        this.items.push(4);
        this.processed = this.doubledItems;

        setTimeout(() => {
          this.processed = this.processed.map(x =>
            this.doubledItems.includes(x) ? x : x * 2
          );
        }, 0);
      }
    }
  });
</script>
```

What will be displayed ?- [2, 4, 6]
- [2, 4, 6, 8]
- [4, 8, 12]
- [2, 4, 6, 16]
Text of the picture (copyable)
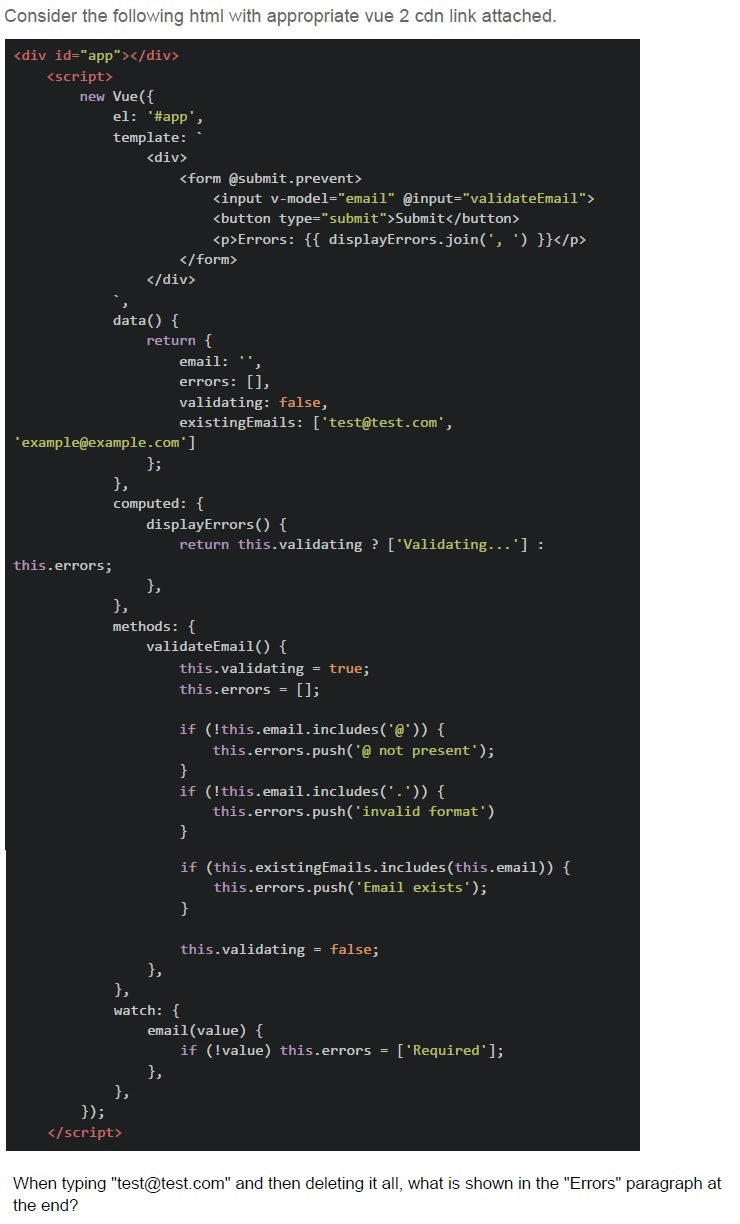
Consider the following html with appropriate vue 2 cdn link attached.

```html
<div id="app"></div>
<script>
  new Vue({
    el: '#app',
    template: `
      <div>
        <form @submit.prevent>
          <input v-model="email" @input="validateEmail">
          <button type="submit">Submit</button>
          <p>Errors: {{ displayErrors.join(', ') }}</p>
        </form>
      </div>
    `,
    data() {
      return {
        email: '',
        errors: [],
        validating: false,
        existingEmails: ['test@test.com', 'example@example.com']
      };
    },
    computed: {
      displayErrors() {
        return this.validating ? ['Validating...'] :
          this.errors;
      }
    },
    methods: {
      validateEmail() {
        this.validating = true;
        this.errors = [];

        if (!this.email.includes('@')) {
          this.errors.push('@ not present');
        }
        if (!this.email.includes('.')) {
          this.errors.push('invalid format');
        }

        if (this.existingEmails.includes(this.email)) {
          this.errors.push('Email exists');
        }

        this.validating = false;
      }
    },
    watch: {
      email(value) {
        if (!value) this.errors = ['Required']
      }
    }
  });
</script>
```

When typing "test@test.com" and then deleting it all, what is shown in the "Errors" paragraph at the end?- Required
- Invalid format, Email exists, Required
- Required, Email exists
- Validating..., Required
Text of the picture (copyable)
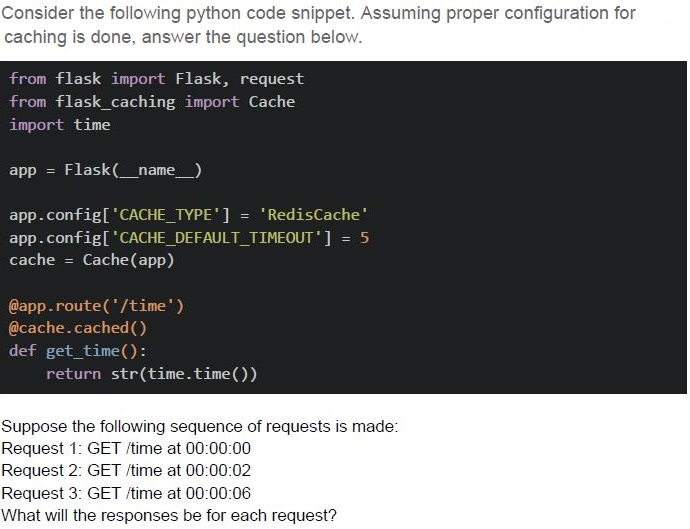
Consider the following python code snippet. Assuming proper configuration for caching is done, answer the question below.

```python
from flask import Flask, request
from flask_caching import Cache
import time

app = Flask(__name__)

app.config['CACHE_TYPE'] = 'RedisCache'
app.config['CACHE_DEFAULT_TIMEOUT'] = 5
cache = Cache(app)

@app.route('/time')
@cache.cached()
def get_time():
    return str(time.time())
```

Suppose the following sequence of requests is made:
Request 1: GET /time at 00:00:00
Request 2: GET /time at 00:00:02
Request 3: GET /time at 00:00:06
What will the responses be for each request?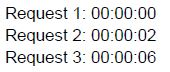
text
Request 1: 00:00:00
Request 2: 00:00:02
Request 3: 00:00:06
text
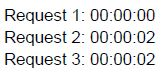
Request 1: 00:00:00
Request 2: 00:00:02
Request 3: 00:00:02
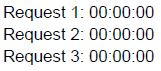
text
Request 1: 00:00:00
Request 2: 00:00:00
Request 3: 00:00:00
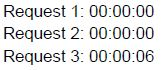
text
Request 1: 00:00:00
Request 2: 00:00:00
Request 3: 00:00:06
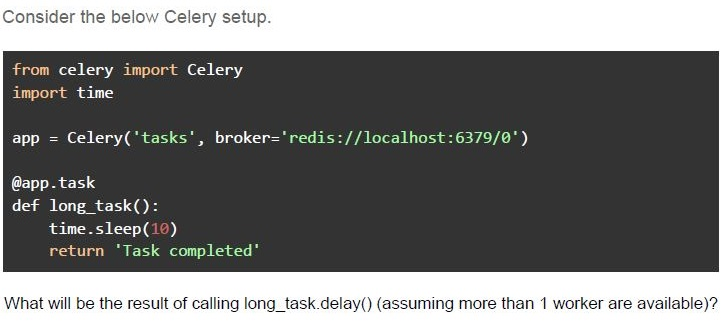
Text of the picture (copyable)
Consider the below Celery setup.

```python
from celery import Celery
import time

app = Celery('tasks', broker='redis://localhost:6379/0')

@app.task
def long_task():
    time.sleep(10)
    return 'Task completed'
```

What will be the result of calling long_task.delay() (assuming more than 1 worker are available)?- The task will immediately execute and print the result 'Task completed'.
- The task will execute asynchronously, and 'Task completed' will be printedafter a 10-second delay.
- The task will execute synchronously, blocking the main thread for 10 seconds.
- None of these
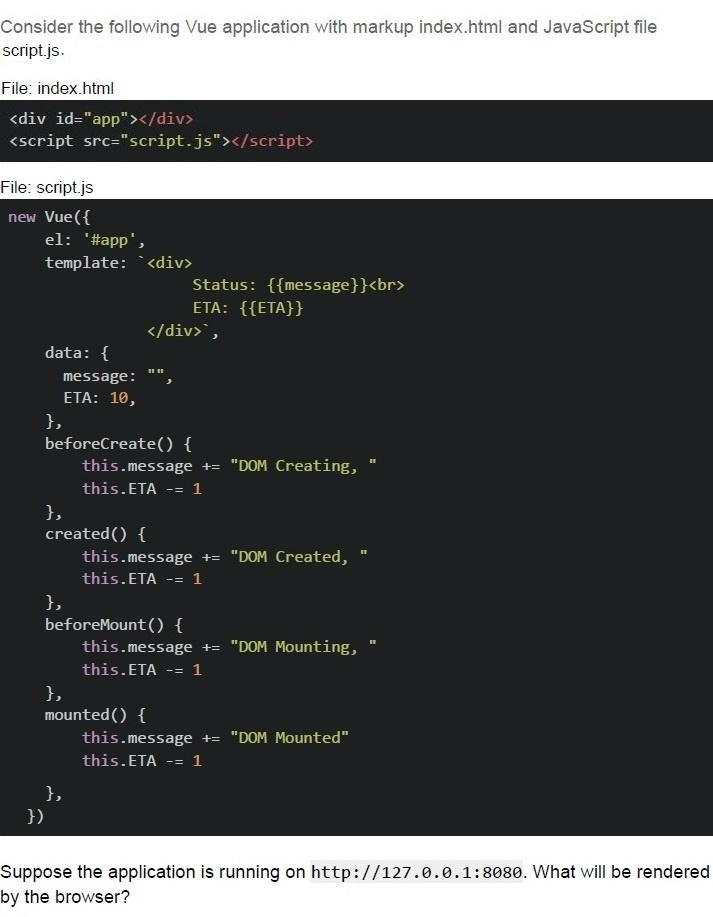
Text of the picture (copyable)
Consider the following Vue application with markup index.html and JavaScript file script.js.

File: index.html
```html
<div id="app"></div>
<script src="script.js"></script>
```

File: script.js
```javascript
new Vue({
    el: '#app',
    template: `<div>
        Status: {{message}}<br>
        ETA: {{ETA}}
    </div>`,

    data: {
        message: "",
        ETA: 10,
    },

    beforeCreate() {
        this.message += "DOM Creating,"
        this.ETA -= 1
    },

    created() {
        this.message += "DOM Created,"
        this.ETA -= 1
    },

    beforeMount() {
        this.message += "DOM Mounting,"
        this.ETA -= 1
    },

    mounted() {
        this.message += "DOM Mounted"
        this.ETA -= 1
    },
})
```

Suppose the application is running on http://127.0.0.1:8080. What will be rendered by the browser?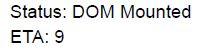
text
Status: DOM Mounted
ETA: 9
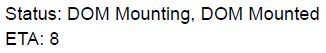
text
Status: DOM Mounting, DOM Mounted
ETA: 8
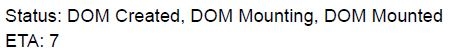
text
Status: DOM Created, DOM Mounting, DOM Mounted
ETA: 7

text
Status: DOM Creating, DOM Created, DOM Mounting, DOM Mounted
ETA: 6
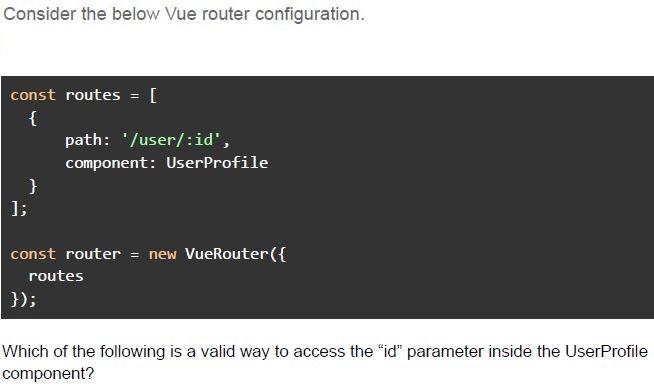
Text of the picture (copyable)
Consider the below Vue router configuration.

```javascript
const routes = [
  {
    path: '/user/:id',
    component: UserProfile
  }
];

const router = new VueRouter({
  routes
});
```

Which of the following is a valid way to access the "id" parameter inside the UserProfile component?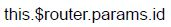
text
```
this.$router.params.id
```
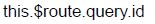
text
```
this.$route.query.id
```
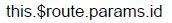
text
```
this.$route.params.id
```
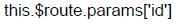
text
```
this.$route.params['id']
```
- Lighthouse measures various performance metrics, including Time toInteractive and Speed Index.
- Lighthouse generates a single score for UI design only.
- It can emulate network throttling and device types during performanceevaluation.
- Lighthouse focuses exclusively on performance and ignores accessibility.
- The local storage data persists even after the browser is closed and reopened.
- The local storage data is automatically cleared every session.
- The local storage can only store strings, and storing objects requires manualserialization and de-serialization.
- Vue's reactivity system automatically updates the local storage when bound toa Vue data property.
Text of the picture (copyable)
Consider the below Vue class binding and select the most appropriate option(s).

```html
<div v-bind:class="[isClassA ? classA : '', classB]"></div>
```
- The class, namely “classB” will always be applied to the div element.
- The classes, namely “classA” and “classB” will always be applied to the divelement.
- The class, namely “classA” will only be applied to the div element, if thevariable “isClassA” evaluates to true.
- The class, namely “classB” will only be applied to the div element, if no variablewith name “isClassA” exists.
- Celery allows web servers to offload long-running tasks to worker processes,decoupling task execution from user requests.
- Push queues are used for real-time operations, while pull queues are bettersuited for batch processing.
- Server-Sent Events (SSE) provide a persistent connection between server andclient, enabling bi-directional communication.
- Redis is a high-performance in-memory database that supports Pub/Sub.
- A Webhook is a method for a server to send real-time data to another serveras an HTTP POST request.
- Webhooks are typically used for sending periodic updates at regular intervals.
- A client must continuously poll a Webhook URL to receive data.
- Webhooks are usually used in event-driven architectures, where an eventtriggers an HTTP POST request to a specified endpoint.
- SSE is a two-way communication protocol, while WebSockets areunidirectional.
- WebSockets are more suited for scenarios requiring bi-directionalcommunication.
- SSE is based on HTTP and can only be used for server-to-client communication,while WebSockets are based on TCP and support both directions.
- SSE is an extension of WebSockets, providing enhanced support for server-to-client communication.
- Processing time-consuming or resource-intensive background jobsasynchronously.
- Directly handling incoming HTTP requests in web servers.
- Scheduling periodic tasks like sending emails or cleaning up the database.
- Serving real-time notifications over WebSockets.
Answer key
- Q1 (MCQ, 3 marks): C
- Q2 (MCQ, 3 marks): B
- Q3 (MCQ, 3 marks): C
- Q4 (MCQ, 3 marks): D
- Q5 (MCQ, 3 marks): B
- Q6 (MCQ, 3 marks): D
- Q7 (MCQ, 3 marks): A
- Q8 (MCQ, 3 marks): B
- Q9 (MCQ, 3 marks): C
- Q10 (MCQ, 3 marks): C
- Q11 (MCQ, 3 marks): A
- Q12 (MCQ, 3 marks): B
- Q13 (MCQ, 2 marks): B
- Q14 (MCQ, 2 marks): B
- Q15 (MCQ, 2 marks): E
- Q16 (MCQ, 2 marks): C
- Q17 (MCQ, 4.5 marks): D
- Q18 (MCQ, 4.5 marks): C
- Q19 (MCQ, 4.5 marks): A
- Q20 (MCQ, 4.5 marks): B
- Q21 (MCQ, 4.5 marks): A
- Q22 (MCQ, 4.5 marks): D
- Q23 (MCQ, 4.5 marks): B
- Q24 (MCQ, 4.5 marks): C
- Q25 (MSQ, 2 marks): C, D
- Q26 (MSQ, 2 marks): A, C
- Q27 (MSQ, 2 marks): A, C
- Q28 (MSQ, 2 marks): A, C
- Q29 (MSQ, 3 marks): A, B, D
- Q30 (MSQ, 3 marks): A, D
- Q31 (MSQ, 3 marks): B, C
- Q32 (MSQ, 3 marks): A, C
Concepts this paper tests
Auto-generated summary from the source site. Handy as a checklist; the lessons above explain each idea from scratch.
Here’s a structured summary of core topics, concepts, principles, and equations for the "Diploma Level: Modern Application Development II" exam, along with Mermaid knowledge graphs to visualize relationships.
Core Topics & Concepts
1. Web Security & Cookies
Key Concepts:
Cookie Attributes:
secure=True: Ensures cookies are sent only over HTTPS.samesite='Strict'|'Lax'|'None': Restricts cross-site requests (CSRF protection).Strict: Cookie sent only for same-site requests.Lax: Default; allows top-level navigations.None: Allows cross-site but requiressecure=True.
httponly: Prevents JavaScript access (mitigates XSS).
Content Security Policy (CSP):
default-src 'self': Restricts resource loading to the same origin.- Blocks external scripts (e.g.,
<script src="https://otherurl.com/code.js">).
Cache-Control Headers:
no-store: Prevents caching entirely.ETag: Validates cache freshness.
Equations/Code Snippets:
// Secure cookie example
response.set_cookie('session_id', 'abc123', secure=True, samesite='Strict');
Content-Security-Policy: default-src 'self';
Cache-Control: no-store2. Asynchronous JavaScript
Key Concepts:
Event Loop:
- Microtasks (Promises) execute before Macrotasks (setTimeout, I/O).
- Order: Sync → Microtasks → Macrotasks.
Promises & Async/Await:
.then()chains handle resolved values..catch()handles rejections.async/await: Syntactic sugar for promises;awaitpauses execution until the promise resolves.- Error Handling: Uncaught promise rejections propagate to
.catch().
- Long Polling vs. WebSockets vs. SSE: | Technique | Direction | Persistence | Use Case | |--------------------|-----------------|-------------|------------------------------| | Long Polling | Client → Server | No | Simulating real-time updates | | WebSockets | Bi-directional | Yes | Chat apps, gaming | | Server-Sent Events | Server → Client | Yes | Live notifications |
Equations/Code Snippets:
// Promise chaining
Promise.resolve(1)
  .then(x => x + 1)
  .then(x => { throw 'error' })
  .catch(e => e + 4)  // Output: "error4"
  .then(x => console.log(x));

// Async/await
async function test() {
  console.log("Start");
  const val = await Promise.resolve(5);  // Pauses here
  console.log(val);  // "5"
  return "End";
}
test().then(data => console.log(data));  // "End"
Output Order (Event Loop):
console.log("Start");
setTimeout(() => console.log("Timeout"), 0);
Promise.resolve().then(() => console.log("Promise"));
console.log("End");
// Output: Start → End → Promise → Timeout
3. Vue.js Core Concepts
Key Concepts:
Lifecycle Hooks:
beforeCreate→created→beforeMount→mounted→beforeUpdate→updated→beforeDestroy→destroyed.
Reactivity:
data()properties are reactive.computedproperties cache results.watchobserves changes (supportsdeep: truefor nested objects).
Slots & Scoped Slots:
<slot name="header" :info="data"></slot>- Consumed via
<template v-slot:header="slotProps">.
Vue Router:
- Dynamic segments:
/profile/:userId→ Access viathis.$route.params.userId. - Wildcard (
*) for 404 routes.
- Dynamic segments:
Vuex:
- State: Single source of truth.
- Actions: Async operations (can
commitmutations). - Mutations: Synchronous state updates.
- Getters: Computed properties for state.
Equations/Code Snippets:
<!-- Scoped slot usage -->
<template v-slot:header="slotProps">
  {{ slotProps.info.title }}
</template>

<!-- Vue Router dynamic param -->
this.$route.params.id  // Access :id
// Vuex action
actions: {
async incrementAsync({ commit }) {
await new Promise(resolve => setTimeout(resolve, 1000));
commit('increment'); // Mutates state
}
}4. HTTP Caching & Storage
Key Concepts:
- Storage Mechanisms: | Type | Persistence | Scope | Size Limit | Access | |---------------|-------------------|-------------|------------|-----------------| |
localStorage| Persists | Per-origin | ~5MB | Sync | |sessionStorage| Session-only | Per-tab | ~5MB | Sync | | Cookies | Configurable | Per-domain | ~4KB | Auto-sent with HTTP | | IndexedDB | Persists | Per-origin | ~50MB+ | Async | Caching Headers:
Cache-Control: max-age=3600(cache for 1 hour).ETag: Validator for conditional requests.
Equations/Code Snippets:
// localStorage usage
localStorage.setItem('cart', JSON.stringify([{ id: 1, name: 'Laptop' }]));
const cart = JSON.parse(localStorage.getItem('cart'));
5. Real-Time Communication
Key Concepts:
WebSockets:
- Full-duplex, low-latency communication.
- Protocol:
ws://orwss://.
Server-Sent Events (SSE):
- Server → Client only (HTTP-based).
- Uses
EventSourceAPI.
Long Polling:
- Client holds connection open until server responds.
Comparison Table:
| Feature | WebSockets | SSE | Long Polling |
|---|---|---|---|
| Direction | Bi-directional | Server → Client | Client → Server |
| Protocol | WS/WSS | HTTP | HTTP |
| Persistence | Yes | Yes | No (per request) |
| Use Case | Chat, gaming | Live updates | Legacy real-time |
6. Task Queues & Background Jobs
Key Concepts:
Celery:
- Distributed task queue for Python.
- Broker: Redis/RabbitMQ.
- Beat: Scheduler for periodic tasks.
- Workers: Execute tasks asynchronously.
Asynchronous Workflow:
- Queue the job.
- Process the job (e.g., data analysis).
- Save results to DB.
- Invoke callback (e.g., webhook).
Equations/Code Snippets:
### Celery periodic task (every 10 minutes)
from celery.schedules import crontab
app.conf.beat_schedule = {
    'send-email-every-10-minutes': {
        'task': 'tasks.send_email',
        'schedule': 600.0,  # 10 minutes in seconds
    },
}
7. Performance Optimization
Key Concepts:
Lighthouse:
- Audits performance, accessibility, SEO, and PWA.
- Metrics: Time to Interactive (TTI), Speed Index, Largest Contentful Paint (LCP).
- Emulates throttling (e.g., 3G network, low-end devices).
Caching Strategies:
- CDN: Distributes static assets globally.
- Redis: In-memory cache for dynamic data.
8. Error Handling & Debugging
Key Concepts:
Vue Error Handling:
errorCapturedlifecycle hook.- Global error handler:
Vue.config.errorHandler.
JavaScript:
try/catchfor synchronous errors..catch()for promises.window.onerrorfor global uncaught errors.
Graph 2: Asynchronous JavaScript
Graph 3: Vue.js Ecosystem
Graph 4: Real-Time Communication
Graph 5: Task Queues & Celery
Graph 6: Storage Mechanisms
Exam Preparation Checklist
Must-Know Topics
- Cookies & Security Headers (
secure,samesite, CSP). - Asynchronous JS (Promises,
async/await, Event Loop). - Vue.js (Reactivity, Lifecycle Hooks, Slots, Vuex, Router).
- HTTP Caching (
Cache-Control,ETag). - Real-Time Tech (WebSockets vs. SSE vs. Long Polling).
- Task Queues (Celery, Redis, Background Jobs).
- Storage APIs (
localStorage,sessionStorage, IndexedDB). - Performance (Lighthouse, Throttling, Caching Strategies).
Key Equations/Code Snippets
| Topic | Code Snippet |
|---|---|
| Secure Cookie | response.set_cookie(..., secure=True, samesite='Strict') |
| Promise Chaining | .then().catch() |
| Vue Scoped Slot | <template v-slot:header="slotProps"> |
| Celery Task | @app.task; celery -A tasks worker --beat |
| localStorage | JSON.parse(localStorage.getItem('key')) |
| CSP Header | Content-Security-Policy: default-src 'self' |
| Vuex Action | async increment({ commit }) { await delay(); commit('mutate') } |
Common Pitfalls
thisBinding: Arrow functions vs. regular functions in Vue/JS.- Vue Reactivity: Direct array/object mutations (use
Vue.setor spread operator). - Async Errors: Unhandled promise rejections crash the app.
- CSP Violations: External scripts blocked if not whitelisted.
- Cache Invalidation: Stale data if
Cache-Controlis misconfigured.